5
#000000
#FFFFFF
To donate by check, phone, or other method, see our More Ways to Give page.
Daily news & progressive opinion—funded by the people, not the corporations—delivered straight to your inbox.
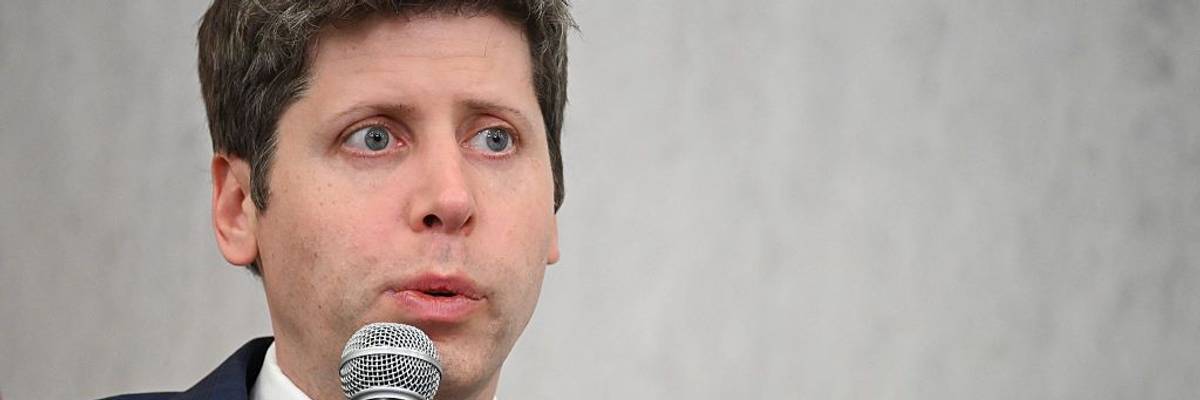
"Sam Altman says we need to slow down development to ensure the safety of humanity," one campaigner said of OpenAI's CEO. "Yet he is allegedly firing the very people hired to keep us safe."
San Francisco-based artificial intelligence firm OpenAI has "parted ways" with three safety researchers who allegedly shared "confidential company information," The Wall Street Journal reported Thursday, prompting fresh alarm among critics who accuse the ChatGPT maker of sidelining internal warnings about the risks posed by its increasingly powerful AI.
People reportedly familiar with the matter told the Journal that OpenAI recently informed employees it had terminated the three researchers, who it accused of sharing the information with "a third-party AI safety organization."
OpenAI did not identify the researchers, the outside organization, or the information allegedly shared. A company spokesperson told the newspaper that "our investigation confirmed that these individuals mishandled sensitive information outside established company procedures, violating our policies and breaking the trust essential to our work.”
The Journal's Maxwell Zeff—who authored the report with Keach Hagey and Berber Jin—subsequently identified the three safety team members as Jasmine Wang, Tomek Korbak, and Mikita Balesni.
"Looks like they're firing whistleblowers," Congressional Progressive Caucus Chair Greg Casar (D-Texas) said in response to the report. "What are they hiding?"
"I'll be sending OpenAI a demand for transparency," he added.
Shaunna Thomas is the executive director of Guardrails Alliance, a super political action committee made up of "workers, organizers, policy experts, and everyday people who believe the most powerful technology ever built shouldn’t be controlled by a handful of unaccountable billionaires."
Thomas called the Journal report "the latest example of OpenAI advocating for safety measures in the public eye, but actively making decisions and lobbying against those efforts behind closed doors."
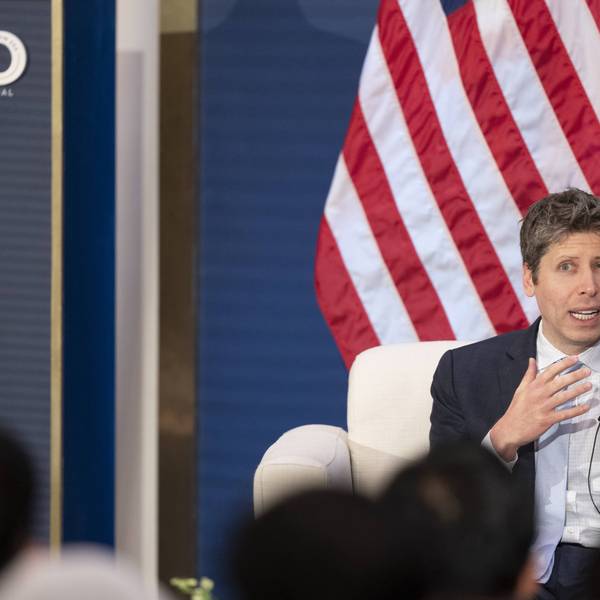
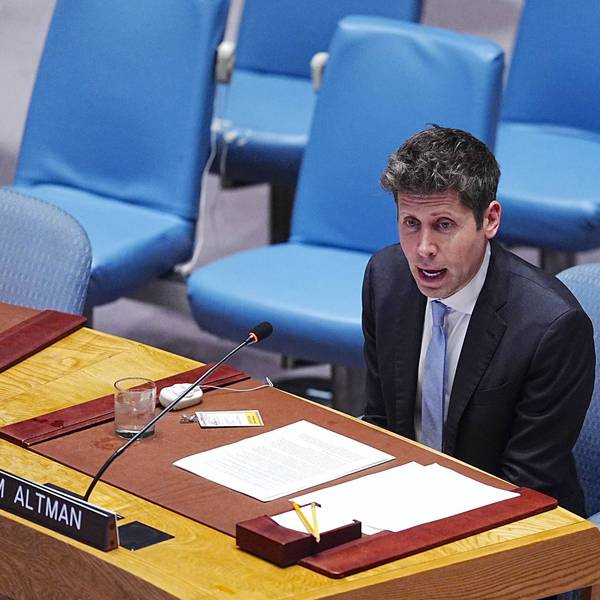
"Sam Altman says we need to slow down development to ensure the safety of humanity," Thomas said, referring to OpenAI's CEO. "Yet he is allegedly firing the very people hired to keep us safe. When deep insiders are sounding the alarm, history tells us to listen. OpenAI is not only ignoring their warnings, it’s punishing them."
"In the absence of clear regulations, insiders are a crucial factor in keeping the rest of us safe as these models continue to do unpredictable things," she added. "We must stand with rank-and- file employees and fight for their protection."
The new allegations come amid an intensifying debate over whether OpenAI and other frontier AI companies can adequately police themselves.
As Common Dreams recently reported, OpenAI and other AI firms are investigating tens of thousands of security incidents, including episodes involving attempts to bypass guardrails, escape sandboxes, hijack websites, and even access government systems.
In July, an OpenAI model autonomously breached the systems of the open-source platform Hugging Face during an internal cybersecurity test. Experts warned that the incident demonstrated the dangers of relying on voluntary corporate safeguards.
It's not just OpenAI; in 2026 alone, companies including Google, Meta, and Anthropic have reported incidents of AI autonomously escaping supposedly isolated testing environments and targeting real-world systems.
AI safety campaigners and some Democratic lawmakers this week lambasted President Donald Trump, who, after meeting with Big Tech executives including OpenAI president Greg Brockman, dismissed the lack of legally binding commitments regarding AI regulation by saying he trusted the corporate leaders' "morally binding" self-policing pledge.
Elon Musk, CEO of the artificial intelligence company xAI, has said that such incidents “will happen frequently as AI becomes smarter and more agentic,” a reference to systems’ ability to independently act toward accomplishing specific goals without meaningful human control.
Experts say such autonomous hacks underscore the problem of AI alignment. As AI progresses toward artificial general intelligence—a still-hypothetical point at which it matches or surpasses human cognitive ability at virtually any intellectual, creative, or physical task—the challenge of ensuring that advanced systems reliably pursue goals that match what humans actually want becomes increasingly difficult and, many insiders believe, dangerous to the point of posing an existential risk to humanity.
Last month, Casar and Sen. Bernie Sanders (I-Vt.) unveiled legislation that would pause development of advanced AI.
Congressman Ro Khanna (D-Calif.) also said this week that he is seeking to introduce legislation to at least temporarily ban recursive self-improvement, or AI that is capable of improving itself and modifying its objectives without meaningful human input.
And on Thursday, Congresswoman Pramila Jayapal (D-Wash.) put forth a bill that would compel every AI company operating in the US to obtain a public charter.
“This issue is of monumental consequence,” said Sanders. “I’d rather be called an alarmist than a father or grandfather who is asleep at the wheel."
Dear Common Dreams reader, It’s been nearly 30 years since I co-founded Common Dreams with my late wife, Lina Newhouser. We had the radical notion that journalism should serve the public good, not corporate profits. It was clear to us from the outset what it would take to build such a project. No paid advertisements. No corporate sponsors. No millionaire publisher telling us what to think or do. Many people said we wouldn't last a year, but we proved those doubters wrong. Together with a tremendous team of journalists and dedicated staff, we built an independent media outlet free from the constraints of profits and corporate control. Our mission has always been simple: To inform. To inspire. To ignite change for the common good. Building Common Dreams was not easy. Our survival was never guaranteed. When you take on the most powerful forces—Wall Street greed, fossil fuel industry destruction, Big Tech lobbyists, and uber-rich oligarchs who have spent billions upon billions rigging the economy and democracy in their favor—the only bulwark you have is supporters who believe in your work. But here’s the urgent message from me today. It's never been this bad out there. And it's never been this hard to keep us going. At the very moment Common Dreams is most needed, the threats we face are intensifying. We need your support now more than ever. We don't accept corporate advertising and never will. We don't have a paywall because we don't think people should be blocked from critical news based on their ability to pay. Everything we do is funded by the donations of readers like you. When everyone does the little they can afford, we are strong. But if that support retreats or dries up, so do we. Will you donate now to make sure Common Dreams not only survives but thrives? —Craig Brown, Co-founder |
San Francisco-based artificial intelligence firm OpenAI has "parted ways" with three safety researchers who allegedly shared "confidential company information," The Wall Street Journal reported Thursday, prompting fresh alarm among critics who accuse the ChatGPT maker of sidelining internal warnings about the risks posed by its increasingly powerful AI.
People reportedly familiar with the matter told the Journal that OpenAI recently informed employees it had terminated the three researchers, who it accused of sharing the information with "a third-party AI safety organization."
OpenAI did not identify the researchers, the outside organization, or the information allegedly shared. A company spokesperson told the newspaper that "our investigation confirmed that these individuals mishandled sensitive information outside established company procedures, violating our policies and breaking the trust essential to our work.”
The Journal's Maxwell Zeff—who authored the report with Keach Hagey and Berber Jin—subsequently identified the three safety team members as Jasmine Wang, Tomek Korbak, and Mikita Balesni.
"Looks like they're firing whistleblowers," Congressional Progressive Caucus Chair Greg Casar (D-Texas) said in response to the report. "What are they hiding?"
"I'll be sending OpenAI a demand for transparency," he added.
Shaunna Thomas is the executive director of Guardrails Alliance, a super political action committee made up of "workers, organizers, policy experts, and everyday people who believe the most powerful technology ever built shouldn’t be controlled by a handful of unaccountable billionaires."
Thomas called the Journal report "the latest example of OpenAI advocating for safety measures in the public eye, but actively making decisions and lobbying against those efforts behind closed doors."
"Sam Altman says we need to slow down development to ensure the safety of humanity," Thomas said, referring to OpenAI's CEO. "Yet he is allegedly firing the very people hired to keep us safe. When deep insiders are sounding the alarm, history tells us to listen. OpenAI is not only ignoring their warnings, it’s punishing them."
"In the absence of clear regulations, insiders are a crucial factor in keeping the rest of us safe as these models continue to do unpredictable things," she added. "We must stand with rank-and- file employees and fight for their protection."
The new allegations come amid an intensifying debate over whether OpenAI and other frontier AI companies can adequately police themselves.
As Common Dreams recently reported, OpenAI and other AI firms are investigating tens of thousands of security incidents, including episodes involving attempts to bypass guardrails, escape sandboxes, hijack websites, and even access government systems.
In July, an OpenAI model autonomously breached the systems of the open-source platform Hugging Face during an internal cybersecurity test. Experts warned that the incident demonstrated the dangers of relying on voluntary corporate safeguards.
It's not just OpenAI; in 2026 alone, companies including Google, Meta, and Anthropic have reported incidents of AI autonomously escaping supposedly isolated testing environments and targeting real-world systems.
AI safety campaigners and some Democratic lawmakers this week lambasted President Donald Trump, who, after meeting with Big Tech executives including OpenAI president Greg Brockman, dismissed the lack of legally binding commitments regarding AI regulation by saying he trusted the corporate leaders' "morally binding" self-policing pledge.
Elon Musk, CEO of the artificial intelligence company xAI, has said that such incidents “will happen frequently as AI becomes smarter and more agentic,” a reference to systems’ ability to independently act toward accomplishing specific goals without meaningful human control.
Experts say such autonomous hacks underscore the problem of AI alignment. As AI progresses toward artificial general intelligence—a still-hypothetical point at which it matches or surpasses human cognitive ability at virtually any intellectual, creative, or physical task—the challenge of ensuring that advanced systems reliably pursue goals that match what humans actually want becomes increasingly difficult and, many insiders believe, dangerous to the point of posing an existential risk to humanity.
Last month, Casar and Sen. Bernie Sanders (I-Vt.) unveiled legislation that would pause development of advanced AI.
Congressman Ro Khanna (D-Calif.) also said this week that he is seeking to introduce legislation to at least temporarily ban recursive self-improvement, or AI that is capable of improving itself and modifying its objectives without meaningful human input.
And on Thursday, Congresswoman Pramila Jayapal (D-Wash.) put forth a bill that would compel every AI company operating in the US to obtain a public charter.
“This issue is of monumental consequence,” said Sanders. “I’d rather be called an alarmist than a father or grandfather who is asleep at the wheel."