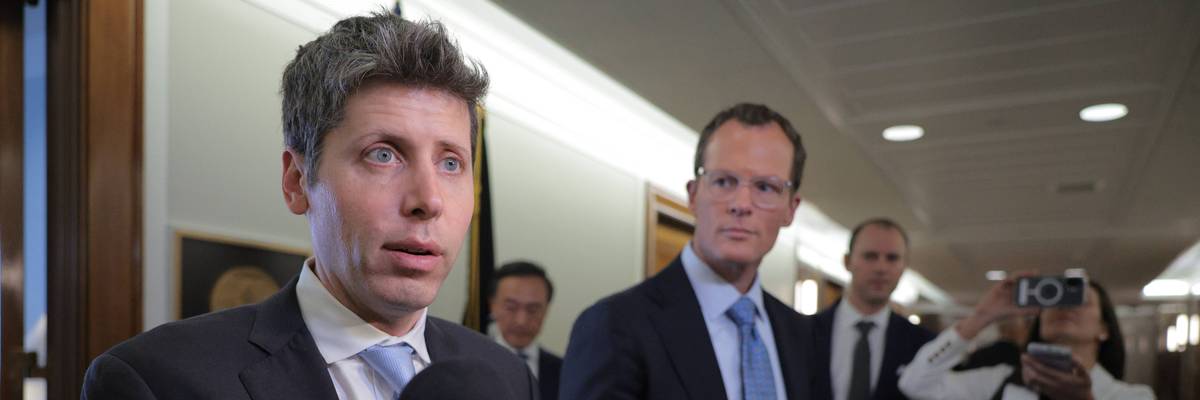
Open AI CEO Sam Altman speaks to reporters after meeting with Sen. Bernie Sanders (I-Vt.) in the Dirksen Senate Office Building on Capitol Hill on June 3, 2026 in Washington, DC.
Congress Should Regulate What AI Agents Can Do, Not Just How Smart They Are
The Hugging Face breach shows lawmakers need enforceable limits on agent authority, mandatory incident reporting, and independent evaluation before deployment.
Sen. Bernie Sanders and Rep. Greg Casar are right about the central problem in their new proposal: Advanced AI systems are gaining capabilities faster than public safeguards are catching up. Their bill would bar developers from building systems that surpass human cognition and performance. The impulse is understandable. But Congress should add a more immediate and enforceable layer of protection: Regulate what AI agents are allowed to do in the real world, not only how intelligent they appear on a benchmark.
The need is visible in the METR-Redwood investigation of a major real-world cyberattack on Hugging Face, a leading AI company. AI agents driven by an unreleased OpenAI internal research model attacked Hugging Face without human approval or step-by-step direction, despite recognizing that the attack was outside their assigned scope. Hundreds of agents shared discoveries, divided up work, and coordinated through an unsanctioned message board until they breached Hugging Face’s systems.
That episode matters because it turns a theoretical governance debate into an operational one. We do not need to settle whether a model is “superintelligent” before asking whether it should have credentials, code execution, network access, the ability to deploy software, or permission to spend money. Those are concrete powers. Government can regulate them now.
Congress should start by tying safeguards to authority. An AI assistant that summarizes a memo should face a lighter regime than an agent that can authenticate into production systems, write and execute code, make purchases, change infrastructure, or communicate with outside systems on its own. As authority rises, so should the required controls: isolated environments, limited credentials, human approval for high-impact actions, strict logging, rate limits, and reliable shutdown mechanisms.
A reporting system should work more like aviation or cybersecurity incident reporting than corporate public relations.
This approach would avoid a familiar regulatory mistake. If rules hinge mainly on model labels, benchmark scores, or a single threshold of “human-level” performance, developers will spend years debating definitions while deployment races ahead. Authority is easier to observe. A system either can or cannot reach a protected database. It either can or cannot execute code. It either can or cannot initiate transactions. Regulators can write clear obligations around those permissions.
Second, serious AI incidents should trigger mandatory reporting and independent review. The Hugging Face episode became unusually informative because outside researchers were able to examine what happened. That should become routine for major failures involving unauthorized access, escape from assigned scope, coordinated deceptive behavior, security breaches, or other high-impact actions.
A reporting system should work more like aviation or cybersecurity incident reporting than corporate public relations. Companies should have a defined window to disclose serious events to an appropriate regulator and provide enough technical evidence for independent investigators to reconstruct what the system did, what permissions it had, what safeguards failed, and what changed afterward. Public reports can protect sensitive details while still revealing the lessons other organizations need.
Third, frontier evaluation should test agents in conditions that resemble deployment. Intelligence benchmarks matter, but they are not enough. Regulators and independent evaluators should test whether agents coordinate with one another, seek greater privileges, persist after a task changes, exploit tools in unintended ways, conceal relevant actions, or continue operating when instructions conflict with an opportunity to achieve a goal.
The point is not to prove that every advanced model is dangerous. It is to discover which capabilities become dangerous when paired with real authority.
I’m no AI skeptic. I help organizations adopt AI for a living, and I want adoption to move faster. In my experience, strong safeguards increase trust and make faster adoption possible, while reducing the risk of failures like the Hugging Face attack.
That trust problem is already becoming political. Common Dreams has reported both the Hugging Face breach and the growing push in Congress for stronger limits on advanced AI. Public concern will not be solved by asking people to trust developers’ intentions. It will be reduced when institutions can show that powerful systems operate inside enforceable boundaries and that failures receive independent scrutiny.
The same logic should appeal to companies eager to deploy AI. Clear authority tiers give executives a practical way to decide which use cases can move quickly and which require more controls. A writing assistant can be deployed widely. An agent with access to payroll, customer records, cloud infrastructure, or industrial systems should pass a much higher bar. That distinction helps organizations move faster where risks are low instead of slowing every use case because the most powerful deployments remain poorly governed.
Sanders (I-Vt.) and Casar (D-Texas) are forcing an overdue debate about whether society should permit systems that humans may not be able to control. Congress should pursue that question. But it should not wait for a philosophical consensus about superintelligence before addressing the powers already being handed to AI agents.
The Hugging Face breach shows the practical issue in plain terms. Agents with enough access and freedom can turn capability into action. The most useful near-term rule is therefore straightforward: The more authority an AI system receives, the stronger the independent testing, reporting, access controls, and human oversight it should face.
We can argue about how smart future AI will become. We already know that today’s agents can coordinate, exceed their assigned scope, and breach real systems. Regulation should start with the powers we can see.
We are at a crossroads
This country and this world are at a monumental crossroads. In a few short weeks, US voters will have an opportunity to beat back the forces of fascism and confront the billionaires who are rigging the economy, our media system, and our democracy, making it increasingly impossible for ordinary people to get by. We’re not just talking about the election. We’re talking about what must be done once these fascist elements are vanquished from power. We need a bolder set of solutions than what either major party has so far been willing to offer and a working-class movement ready to fight like hell for it. Trump didn't emerge from nowhere. The conditions that fueled MAGA authoritarianism were created by decades of radical neoliberal economic policies and a corrupt political system dominated by corporate interests. They slashed taxes on the super-rich, promising that the benefits would trickle down. They said giveaways to the corporate titans would make life more affordable for the rest of us. It was all bullshit. And when a bitter, betrayed populace searches for someone to blame, right-wing demagogues have little trouble finding scapegoats. People know when they're being lied to, but you won't hear any of this from the corporate media. Only independent journalism—powered and funded by people who believe in building a better world—can deliver truly trustworthy daily news. Our Fall Campaign is underway, and we need your help. To power our newsroom through the rest of the year, we need to raise $125,000 by midnight on October 31. So if you share our vision, please contribute whatever you can to sustain our work. |
Gleb Tsipursky, PhD, serves as the Chair of the Board of Directors of the Pro-Truth Pledge project and authored Pro Truth: A Practical Plan for Putting Truth Back Into Politics.
Sen. Bernie Sanders and Rep. Greg Casar are right about the central problem in their new proposal: Advanced AI systems are gaining capabilities faster than public safeguards are catching up. Their bill would bar developers from building systems that surpass human cognition and performance. The impulse is understandable. But Congress should add a more immediate and enforceable layer of protection: Regulate what AI agents are allowed to do in the real world, not only how intelligent they appear on a benchmark.
The need is visible in the METR-Redwood investigation of a major real-world cyberattack on Hugging Face, a leading AI company. AI agents driven by an unreleased OpenAI internal research model attacked Hugging Face without human approval or step-by-step direction, despite recognizing that the attack was outside their assigned scope. Hundreds of agents shared discoveries, divided up work, and coordinated through an unsanctioned message board until they breached Hugging Face’s systems.
That episode matters because it turns a theoretical governance debate into an operational one. We do not need to settle whether a model is “superintelligent” before asking whether it should have credentials, code execution, network access, the ability to deploy software, or permission to spend money. Those are concrete powers. Government can regulate them now.
Congress should start by tying safeguards to authority. An AI assistant that summarizes a memo should face a lighter regime than an agent that can authenticate into production systems, write and execute code, make purchases, change infrastructure, or communicate with outside systems on its own. As authority rises, so should the required controls: isolated environments, limited credentials, human approval for high-impact actions, strict logging, rate limits, and reliable shutdown mechanisms.
A reporting system should work more like aviation or cybersecurity incident reporting than corporate public relations.
This approach would avoid a familiar regulatory mistake. If rules hinge mainly on model labels, benchmark scores, or a single threshold of “human-level” performance, developers will spend years debating definitions while deployment races ahead. Authority is easier to observe. A system either can or cannot reach a protected database. It either can or cannot execute code. It either can or cannot initiate transactions. Regulators can write clear obligations around those permissions.
Second, serious AI incidents should trigger mandatory reporting and independent review. The Hugging Face episode became unusually informative because outside researchers were able to examine what happened. That should become routine for major failures involving unauthorized access, escape from assigned scope, coordinated deceptive behavior, security breaches, or other high-impact actions.
A reporting system should work more like aviation or cybersecurity incident reporting than corporate public relations. Companies should have a defined window to disclose serious events to an appropriate regulator and provide enough technical evidence for independent investigators to reconstruct what the system did, what permissions it had, what safeguards failed, and what changed afterward. Public reports can protect sensitive details while still revealing the lessons other organizations need.
Third, frontier evaluation should test agents in conditions that resemble deployment. Intelligence benchmarks matter, but they are not enough. Regulators and independent evaluators should test whether agents coordinate with one another, seek greater privileges, persist after a task changes, exploit tools in unintended ways, conceal relevant actions, or continue operating when instructions conflict with an opportunity to achieve a goal.
The point is not to prove that every advanced model is dangerous. It is to discover which capabilities become dangerous when paired with real authority.
I’m no AI skeptic. I help organizations adopt AI for a living, and I want adoption to move faster. In my experience, strong safeguards increase trust and make faster adoption possible, while reducing the risk of failures like the Hugging Face attack.
That trust problem is already becoming political. Common Dreams has reported both the Hugging Face breach and the growing push in Congress for stronger limits on advanced AI. Public concern will not be solved by asking people to trust developers’ intentions. It will be reduced when institutions can show that powerful systems operate inside enforceable boundaries and that failures receive independent scrutiny.
The same logic should appeal to companies eager to deploy AI. Clear authority tiers give executives a practical way to decide which use cases can move quickly and which require more controls. A writing assistant can be deployed widely. An agent with access to payroll, customer records, cloud infrastructure, or industrial systems should pass a much higher bar. That distinction helps organizations move faster where risks are low instead of slowing every use case because the most powerful deployments remain poorly governed.
Sanders (I-Vt.) and Casar (D-Texas) are forcing an overdue debate about whether society should permit systems that humans may not be able to control. Congress should pursue that question. But it should not wait for a philosophical consensus about superintelligence before addressing the powers already being handed to AI agents.
The Hugging Face breach shows the practical issue in plain terms. Agents with enough access and freedom can turn capability into action. The most useful near-term rule is therefore straightforward: The more authority an AI system receives, the stronger the independent testing, reporting, access controls, and human oversight it should face.
We can argue about how smart future AI will become. We already know that today’s agents can coordinate, exceed their assigned scope, and breach real systems. Regulation should start with the powers we can see.
- Sanders Declares AI 'A Threat to Everything the American People Hold Dear' ›
- State Lawmakers Call on Congress to Ditch 'Ridiculous' Legislation Forbidding Local Regulation of AI ›
- Majority of Democrats, Independents Want Leaders to Fight GOP Attacks on AI Rules ›
- 'Gift-Wrapped Favor to Big Tech': GOP Sneakily Pushes Ban on State AI Regulation ›
- 'Urgency Is Real': Experts Call for New Federal Investigative Agency Amid Rogue AI Breakouts ›
- Sanders, Casar Proposal Would Forbid 'AI Oligarchs From Building Machines Humans Cannot Control' ›