SUBSCRIBE TO OUR FREE NEWSLETTER
Daily news & progressive opinion—funded by the people, not the corporations—delivered straight to your inbox.
5
#000000
#FFFFFF
To donate by check, phone, or other method, see our More Ways to Give page.
It's official: The Cyber Intelligence Sharing and Protection Act was reintroduced in the House of Representatives yesterday. CISPA is the contentious bill civil liberties advocates fought last year, which would provide a poorly-defined "cybersecurity" exception to existing privacy law. CISPA offers broad immunities to companies who choose to share data with government agencies (including the private communications of users) in the name of cybersecurity. It also creates avenues for companies to share data with any
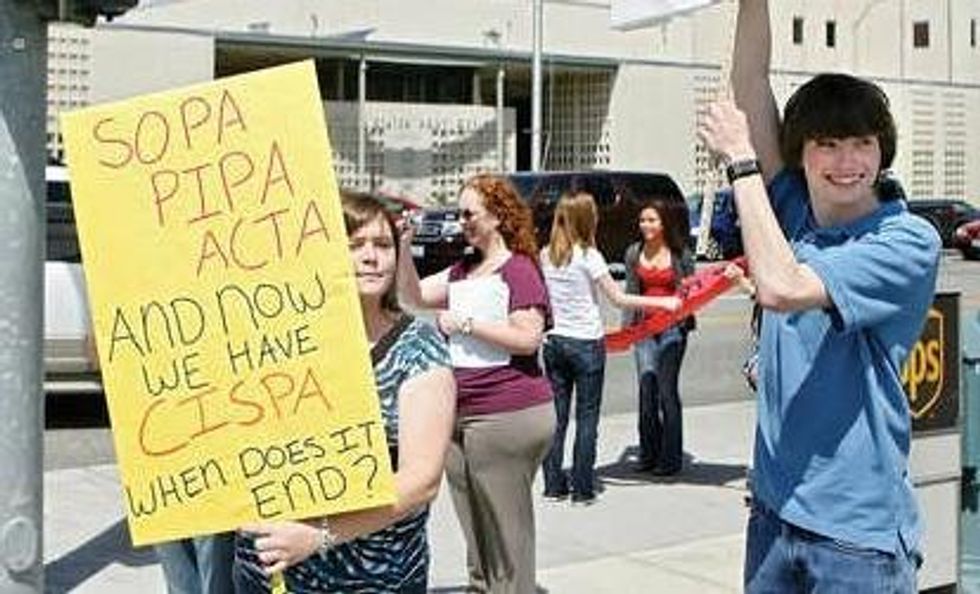
EFF is adamantly opposed to CISPA. Will you join us in calling on Congress to stop this and any other privacy-invasive cybersecurity legislation?
As others have noted, "CISPA is deeply flawed. Under a broad cybersecurity umbrella, it permits companies to share user communications directly with the super secret NSA and permits the NSA to use that information for non-cybersecurity reasons. This risks turning the cybersecurity program into a back door intelligence surveillance program run by a military entity with little transparency or public accountability."
Last year, CISPA passed the House with a few handful of amendments that tried to fix some of its vague language. But the amendments didn't address many of the significant civil liberties concerns. Those remaining problems were reintroduced in today's version of CISPA. Here's a brief overview of the issues:
Companies have new rights to monitor user actions and share data--including potentially sensitive user data--with the government without a warrant.
First, CISPA would still give businesses1 the power to use "cybersecurity systems" to obtain any "cybersecurity threat information" (CTI)--which could include personal communications--about a perceived threat to their networks or systems. The only limitation is that the company must act for a "cybersecurity purpose," which is vaguely defined to include such things as "safeguarding" networks.
CISPA overrides existing privacy law, and grants broad immunities to participating companies.
At the same time, CISPA would also create a broad immunity from legal liability for monitoring, acquiring, or sharing CTI, so long as the entity acted "in good faith." Our concern from day one has been that these combined power and immunity provisions would override existing privacy laws like the Wiretap Act and the Stored Communications Act.
Worse, the law provides immunity "for decisions made based on" CTI. A rogue or misguided company could easily make bad "decisions" that would do a lot more harm than good, and should not be immunized.
CISPA also raises major transparency and accountability issues.
Information provided to the federal government under CISPA would be exempt from the Freedom of Information Act (FOIA) and other state laws that could otherwise require disclosure (unless some law other than CISPA already requires its provision to the government).
Users probably won't know if their private data is compromised under CISPA, and will have little recourse.
CISPA's authors argue that the bill contains limitations on how the federal government can use and disclose information by permitting lawsuits against the government. But if a company sends information about a user that is not cyberthreat information, the government agency does not notify the user, only the company.
CISPA is a dangerous bill
These are just a couple of reasons of why CISPA is a dangerous bill and why President Obama threatened to veto the bill last year. CISPA essentially equates greater cybersecurity with greater surveillance and information sharing. But many of our cybersecurity problems arise from software vulnerabilities and human failings, issues CISPA fails to address. For instance, the recent series of hackssuffered by New York Timeswere suspected to be from spearphishing and victims downloading malicious software masked as email attachments--the types of issues that CISPA doesn't deal with.
We were heartened to hear that President Obama's new Executive Order on cybersecurity will encourage government agencies to more readily share cybersecurity information with companies, and may even reduce unnecessary secrecy around cybersecurity information. Let's use the momentum from the Executive Order to turn a new leaf in the cybersecurity debate, beginning a broader public dialogue about cybersecurity that doesn't assume that surveillance is the right solution.
Please join EFF in opposing CISPA by contacting Congress today.
It's official: The Cyber Intelligence Sharing and Protection Act was reintroduced in the House of Representatives yesterday. CISPA is the contentious bill civil liberties advocates fought last year, which would provide a poorly-defined "cybersecurity" exception to existing privacy law. CISPA offers broad immunities to companies who choose to share data with government agencies (including the private communications of users) in the name of cybersecurity. It also creates avenues for companies to share data with any
EFF is adamantly opposed to CISPA. Will you join us in calling on Congress to stop this and any other privacy-invasive cybersecurity legislation?
As others have noted, "CISPA is deeply flawed. Under a broad cybersecurity umbrella, it permits companies to share user communications directly with the super secret NSA and permits the NSA to use that information for non-cybersecurity reasons. This risks turning the cybersecurity program into a back door intelligence surveillance program run by a military entity with little transparency or public accountability."
Last year, CISPA passed the House with a few handful of amendments that tried to fix some of its vague language. But the amendments didn't address many of the significant civil liberties concerns. Those remaining problems were reintroduced in today's version of CISPA. Here's a brief overview of the issues:
Companies have new rights to monitor user actions and share data--including potentially sensitive user data--with the government without a warrant.
First, CISPA would still give businesses1 the power to use "cybersecurity systems" to obtain any "cybersecurity threat information" (CTI)--which could include personal communications--about a perceived threat to their networks or systems. The only limitation is that the company must act for a "cybersecurity purpose," which is vaguely defined to include such things as "safeguarding" networks.
CISPA overrides existing privacy law, and grants broad immunities to participating companies.
At the same time, CISPA would also create a broad immunity from legal liability for monitoring, acquiring, or sharing CTI, so long as the entity acted "in good faith." Our concern from day one has been that these combined power and immunity provisions would override existing privacy laws like the Wiretap Act and the Stored Communications Act.
Worse, the law provides immunity "for decisions made based on" CTI. A rogue or misguided company could easily make bad "decisions" that would do a lot more harm than good, and should not be immunized.
CISPA also raises major transparency and accountability issues.
Information provided to the federal government under CISPA would be exempt from the Freedom of Information Act (FOIA) and other state laws that could otherwise require disclosure (unless some law other than CISPA already requires its provision to the government).
Users probably won't know if their private data is compromised under CISPA, and will have little recourse.
CISPA's authors argue that the bill contains limitations on how the federal government can use and disclose information by permitting lawsuits against the government. But if a company sends information about a user that is not cyberthreat information, the government agency does not notify the user, only the company.
CISPA is a dangerous bill
These are just a couple of reasons of why CISPA is a dangerous bill and why President Obama threatened to veto the bill last year. CISPA essentially equates greater cybersecurity with greater surveillance and information sharing. But many of our cybersecurity problems arise from software vulnerabilities and human failings, issues CISPA fails to address. For instance, the recent series of hackssuffered by New York Timeswere suspected to be from spearphishing and victims downloading malicious software masked as email attachments--the types of issues that CISPA doesn't deal with.
We were heartened to hear that President Obama's new Executive Order on cybersecurity will encourage government agencies to more readily share cybersecurity information with companies, and may even reduce unnecessary secrecy around cybersecurity information. Let's use the momentum from the Executive Order to turn a new leaf in the cybersecurity debate, beginning a broader public dialogue about cybersecurity that doesn't assume that surveillance is the right solution.
Please join EFF in opposing CISPA by contacting Congress today.
It's official: The Cyber Intelligence Sharing and Protection Act was reintroduced in the House of Representatives yesterday. CISPA is the contentious bill civil liberties advocates fought last year, which would provide a poorly-defined "cybersecurity" exception to existing privacy law. CISPA offers broad immunities to companies who choose to share data with government agencies (including the private communications of users) in the name of cybersecurity. It also creates avenues for companies to share data with any
EFF is adamantly opposed to CISPA. Will you join us in calling on Congress to stop this and any other privacy-invasive cybersecurity legislation?
As others have noted, "CISPA is deeply flawed. Under a broad cybersecurity umbrella, it permits companies to share user communications directly with the super secret NSA and permits the NSA to use that information for non-cybersecurity reasons. This risks turning the cybersecurity program into a back door intelligence surveillance program run by a military entity with little transparency or public accountability."
Last year, CISPA passed the House with a few handful of amendments that tried to fix some of its vague language. But the amendments didn't address many of the significant civil liberties concerns. Those remaining problems were reintroduced in today's version of CISPA. Here's a brief overview of the issues:
Companies have new rights to monitor user actions and share data--including potentially sensitive user data--with the government without a warrant.
First, CISPA would still give businesses1 the power to use "cybersecurity systems" to obtain any "cybersecurity threat information" (CTI)--which could include personal communications--about a perceived threat to their networks or systems. The only limitation is that the company must act for a "cybersecurity purpose," which is vaguely defined to include such things as "safeguarding" networks.
CISPA overrides existing privacy law, and grants broad immunities to participating companies.
At the same time, CISPA would also create a broad immunity from legal liability for monitoring, acquiring, or sharing CTI, so long as the entity acted "in good faith." Our concern from day one has been that these combined power and immunity provisions would override existing privacy laws like the Wiretap Act and the Stored Communications Act.
Worse, the law provides immunity "for decisions made based on" CTI. A rogue or misguided company could easily make bad "decisions" that would do a lot more harm than good, and should not be immunized.
CISPA also raises major transparency and accountability issues.
Information provided to the federal government under CISPA would be exempt from the Freedom of Information Act (FOIA) and other state laws that could otherwise require disclosure (unless some law other than CISPA already requires its provision to the government).
Users probably won't know if their private data is compromised under CISPA, and will have little recourse.
CISPA's authors argue that the bill contains limitations on how the federal government can use and disclose information by permitting lawsuits against the government. But if a company sends information about a user that is not cyberthreat information, the government agency does not notify the user, only the company.
CISPA is a dangerous bill
These are just a couple of reasons of why CISPA is a dangerous bill and why President Obama threatened to veto the bill last year. CISPA essentially equates greater cybersecurity with greater surveillance and information sharing. But many of our cybersecurity problems arise from software vulnerabilities and human failings, issues CISPA fails to address. For instance, the recent series of hackssuffered by New York Timeswere suspected to be from spearphishing and victims downloading malicious software masked as email attachments--the types of issues that CISPA doesn't deal with.
We were heartened to hear that President Obama's new Executive Order on cybersecurity will encourage government agencies to more readily share cybersecurity information with companies, and may even reduce unnecessary secrecy around cybersecurity information. Let's use the momentum from the Executive Order to turn a new leaf in the cybersecurity debate, beginning a broader public dialogue about cybersecurity that doesn't assume that surveillance is the right solution.
Please join EFF in opposing CISPA by contacting Congress today.