SUBSCRIBE TO OUR FREE NEWSLETTER
Daily news & progressive opinion—funded by the people, not the corporations—delivered straight to your inbox.
5
#000000
#FFFFFF
To donate by check, phone, or other method, see our More Ways to Give page.
Daily news & progressive opinion—funded by the people, not the corporations—delivered straight to your inbox.
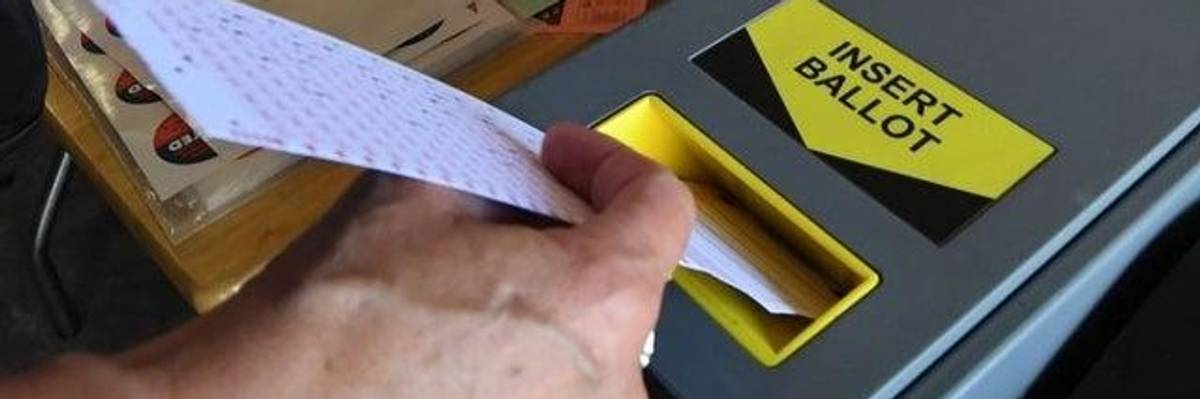
Despite long-standing reassurances by vendors and election officials that voting machines cannot be hacked because they are not connected to the internet, recent security reports reveal that many voting machines are connected to the internet and possibly have been for years. (Photo: Getty)
As the election security conversation widens beyond Russia, to include countries like Iran and China, it's important to examine how security flaws in our country's voting equipment increase the vulnerability of our elections.
In 2010 a university cyber team conducted a test attack on an internet voting pilot project in Washington, D.C. The team successfully picked the winner of the election remotely from its Michigan lab. Writing about the attack, computer science professor J. Alex Halderman said, "Within 36 hours of the system going live, our team had ... the ability to change votes."
In follow-up testimony, Halderman offered some chilling details: "While we were in control of these systems, we observed other attack attempts originating from computers in Iran and China. These attackers were attempting to guess the same master password that we did. And since it was only four letters long, they would likely have soon succeeded."
Security experts have long warned that short passwords provide easy targets, but hackers at DEF CON, an annual security convention, recently found U.S. election systems with no passwords at all.
How did the security bar get set so low?
"Right now there are no mandatory federal cybersecurity standards for elections," Sen. Ron Wyden (D-Ore.) reported in a July speech. "It is perfectly legal for the biggest voting machine company in America ... to sell a small county equipment that every cyber-security expert in America knows is insecure."
For a perfect example of this, look at Louisiana, where the secretary of state's office purchased touch screen ballot-marking devices for parishes across the state. Some election experts warn that ballot-marking devices have serious reliability and security issues, and recommend they be used only for voters who are unable to mark a ballot by hand. Studies detail how most voters do not check ballots from these systems, opening the door for ballots to be printed with the wrong candidates.
Some states also use QR codes to count votes. Concerns that barcodes or QR codes could be used to change results led Colorado to ban their use in counting votes. Nevertheless, barcode ballot-marking devices are being sold from Wisconsin to Georgia. One reason? They are among the most expensive systems on the market, allowing a higher profit for vendors. Comparison studies indicate that using a barcode ballot-marking system for all voters can double or triple costs.
Researchers continue to discover ongoing security issues with the voting machine industry, including poor internal company security. In 2017, the largest U.S. voting machine vendor, ES&S, exposed encrypted employee passwords online. Using those passwords, hackers could have planted malware on the company's servers, and that malware could then be delivered to voting systems across the country with official updates. "This is the type of stuff that leads to a complete compromise," said cyber-risk analyst Chris Vickery.
Both ES&S and its main competitor, Dominion Voting Systems, have released voting machines that security experts say can add votes to paper ballots after they are cast by voters.
Together, these two companies sell and maintain 80 percent of U.S. voting systems.
Despite long-standing reassurances by vendors and election officials that voting machines cannot be hacked because they are not connected to the internet, recent security reports reveal that many voting machines are connected to the internet and possibly have been for years. Security experts are alarmed at internet connectivity in voting systems because it can allow hackers to inject malware that disrupts or changes the outcome of an election.
Kevin Skoglund, the lead researcher of one study, confirmed that vendors "know their systems are connecting through the internet."
In August, North Carolina became the latest casualty. Voters and representatives from good-government groups pleaded with the state board of elections to adopt the type of voting system almost unanimously supported by election security experts, one that uses hand-marked paper ballots. They asked the board to reject ballot-marking devices that use barcodes and argued that hand-marked paper ballots are more secure, less expensive and less likely to create long lines at the polls.
Nevertheless, Democratic chair Damon Circosta reached across the aisle to join two Republican commissioners in opening the North Carolina market to a barcode ballot-marking system. The vote presents a setback to a multi-year effort to provide secure, accurate elections for North Carolina voters.
Similar decisions have been made in Delaware, Georgia, Kansas, New York, Pennsylvania and Wisconsin. Communities in those states have experienced frustration, outrage and even launched investigations following certification or adoption of election systems opposed by experts, good-government groups, competing vendors and the general public. South Carolina lawmakers initially balked at the high price and poor security of new voting machines but eventually capitulated.
Some of these systems have subsequently had disastrous debuts, as in the case of Johnson County, Kansas, where, after spending $10.5 million on a new touch screen barcode voting system, the county experienced an election night alternately called a debacle and a fiasco.
How are vendors achieving these wins against such strong opposition? Jennifer Cohn, an election security advocate, has detailed many of the techniques being used. They include deep ties to powerful political players, targeted donations to political parties and their leaders, and cozy relationships with election officials that can include gifts, dining and travel. The newly released Philadelphia City Controller's report details conflicts of interest that resulted in a $2.9 million fine for the vendor, but the $29 million voting machine contract remains intact.
Are these insecure voting systems actually leading to incorrect election results? Perhaps. A 2015 election in Memphis, Tenn., underreported votes in four predominantly black precincts; data suggest over 100,000 votes may be missing from a Georgia election held last year.
The Senate has passed $250 million in funding for election security. Missing from the bill? Any language requiring strong security. Legislation has been proposed that would put real safeguards in place for our elections. It is even more imperative that it be passed now.
This country and this world are at a monumental crossroads. US voters have an opportunity to beat back the forces of fascism and confront the billionaires who are rigging the economy, our media system, and our democracy, making it increasingly impossible for ordinary people to get by. We’re not just talking about the election. We’re talking about what must be done once these fascist elements are vanquished from power. We need a bolder set of solutions than what either major party has so far been willing to offer and a working-class movement ready to fight like hell for it. Trump didn't emerge from nowhere. The conditions that fueled MAGA authoritarianism were created by decades of radical neoliberal economic policies and a corrupt political system dominated by corporate interests. They slashed taxes on the super-rich, promising that the benefits would trickle down. They said giveaways to the corporate titans would make life more affordable for the rest of us. It was all bullshit. And when a bitter, betrayed populace searches for someone to blame, right-wing demagogues have little trouble finding scapegoats. People know when they're being lied to, but you won't hear any of this from the corporate media. Only independent journalism—powered and funded by people who believe in building a better world—can deliver truly trustworthy daily news. If you share our vision, please contribute whatever you can to sustain our work. |
As the election security conversation widens beyond Russia, to include countries like Iran and China, it's important to examine how security flaws in our country's voting equipment increase the vulnerability of our elections.
In 2010 a university cyber team conducted a test attack on an internet voting pilot project in Washington, D.C. The team successfully picked the winner of the election remotely from its Michigan lab. Writing about the attack, computer science professor J. Alex Halderman said, "Within 36 hours of the system going live, our team had ... the ability to change votes."
In follow-up testimony, Halderman offered some chilling details: "While we were in control of these systems, we observed other attack attempts originating from computers in Iran and China. These attackers were attempting to guess the same master password that we did. And since it was only four letters long, they would likely have soon succeeded."
Security experts have long warned that short passwords provide easy targets, but hackers at DEF CON, an annual security convention, recently found U.S. election systems with no passwords at all.
How did the security bar get set so low?
"Right now there are no mandatory federal cybersecurity standards for elections," Sen. Ron Wyden (D-Ore.) reported in a July speech. "It is perfectly legal for the biggest voting machine company in America ... to sell a small county equipment that every cyber-security expert in America knows is insecure."
For a perfect example of this, look at Louisiana, where the secretary of state's office purchased touch screen ballot-marking devices for parishes across the state. Some election experts warn that ballot-marking devices have serious reliability and security issues, and recommend they be used only for voters who are unable to mark a ballot by hand. Studies detail how most voters do not check ballots from these systems, opening the door for ballots to be printed with the wrong candidates.
Some states also use QR codes to count votes. Concerns that barcodes or QR codes could be used to change results led Colorado to ban their use in counting votes. Nevertheless, barcode ballot-marking devices are being sold from Wisconsin to Georgia. One reason? They are among the most expensive systems on the market, allowing a higher profit for vendors. Comparison studies indicate that using a barcode ballot-marking system for all voters can double or triple costs.
Researchers continue to discover ongoing security issues with the voting machine industry, including poor internal company security. In 2017, the largest U.S. voting machine vendor, ES&S, exposed encrypted employee passwords online. Using those passwords, hackers could have planted malware on the company's servers, and that malware could then be delivered to voting systems across the country with official updates. "This is the type of stuff that leads to a complete compromise," said cyber-risk analyst Chris Vickery.
Both ES&S and its main competitor, Dominion Voting Systems, have released voting machines that security experts say can add votes to paper ballots after they are cast by voters.
Together, these two companies sell and maintain 80 percent of U.S. voting systems.
Despite long-standing reassurances by vendors and election officials that voting machines cannot be hacked because they are not connected to the internet, recent security reports reveal that many voting machines are connected to the internet and possibly have been for years. Security experts are alarmed at internet connectivity in voting systems because it can allow hackers to inject malware that disrupts or changes the outcome of an election.
Kevin Skoglund, the lead researcher of one study, confirmed that vendors "know their systems are connecting through the internet."
In August, North Carolina became the latest casualty. Voters and representatives from good-government groups pleaded with the state board of elections to adopt the type of voting system almost unanimously supported by election security experts, one that uses hand-marked paper ballots. They asked the board to reject ballot-marking devices that use barcodes and argued that hand-marked paper ballots are more secure, less expensive and less likely to create long lines at the polls.
Nevertheless, Democratic chair Damon Circosta reached across the aisle to join two Republican commissioners in opening the North Carolina market to a barcode ballot-marking system. The vote presents a setback to a multi-year effort to provide secure, accurate elections for North Carolina voters.
Similar decisions have been made in Delaware, Georgia, Kansas, New York, Pennsylvania and Wisconsin. Communities in those states have experienced frustration, outrage and even launched investigations following certification or adoption of election systems opposed by experts, good-government groups, competing vendors and the general public. South Carolina lawmakers initially balked at the high price and poor security of new voting machines but eventually capitulated.
Some of these systems have subsequently had disastrous debuts, as in the case of Johnson County, Kansas, where, after spending $10.5 million on a new touch screen barcode voting system, the county experienced an election night alternately called a debacle and a fiasco.
How are vendors achieving these wins against such strong opposition? Jennifer Cohn, an election security advocate, has detailed many of the techniques being used. They include deep ties to powerful political players, targeted donations to political parties and their leaders, and cozy relationships with election officials that can include gifts, dining and travel. The newly released Philadelphia City Controller's report details conflicts of interest that resulted in a $2.9 million fine for the vendor, but the $29 million voting machine contract remains intact.
Are these insecure voting systems actually leading to incorrect election results? Perhaps. A 2015 election in Memphis, Tenn., underreported votes in four predominantly black precincts; data suggest over 100,000 votes may be missing from a Georgia election held last year.
The Senate has passed $250 million in funding for election security. Missing from the bill? Any language requiring strong security. Legislation has been proposed that would put real safeguards in place for our elections. It is even more imperative that it be passed now.
As the election security conversation widens beyond Russia, to include countries like Iran and China, it's important to examine how security flaws in our country's voting equipment increase the vulnerability of our elections.
In 2010 a university cyber team conducted a test attack on an internet voting pilot project in Washington, D.C. The team successfully picked the winner of the election remotely from its Michigan lab. Writing about the attack, computer science professor J. Alex Halderman said, "Within 36 hours of the system going live, our team had ... the ability to change votes."
In follow-up testimony, Halderman offered some chilling details: "While we were in control of these systems, we observed other attack attempts originating from computers in Iran and China. These attackers were attempting to guess the same master password that we did. And since it was only four letters long, they would likely have soon succeeded."
Security experts have long warned that short passwords provide easy targets, but hackers at DEF CON, an annual security convention, recently found U.S. election systems with no passwords at all.
How did the security bar get set so low?
"Right now there are no mandatory federal cybersecurity standards for elections," Sen. Ron Wyden (D-Ore.) reported in a July speech. "It is perfectly legal for the biggest voting machine company in America ... to sell a small county equipment that every cyber-security expert in America knows is insecure."
For a perfect example of this, look at Louisiana, where the secretary of state's office purchased touch screen ballot-marking devices for parishes across the state. Some election experts warn that ballot-marking devices have serious reliability and security issues, and recommend they be used only for voters who are unable to mark a ballot by hand. Studies detail how most voters do not check ballots from these systems, opening the door for ballots to be printed with the wrong candidates.
Some states also use QR codes to count votes. Concerns that barcodes or QR codes could be used to change results led Colorado to ban their use in counting votes. Nevertheless, barcode ballot-marking devices are being sold from Wisconsin to Georgia. One reason? They are among the most expensive systems on the market, allowing a higher profit for vendors. Comparison studies indicate that using a barcode ballot-marking system for all voters can double or triple costs.
Researchers continue to discover ongoing security issues with the voting machine industry, including poor internal company security. In 2017, the largest U.S. voting machine vendor, ES&S, exposed encrypted employee passwords online. Using those passwords, hackers could have planted malware on the company's servers, and that malware could then be delivered to voting systems across the country with official updates. "This is the type of stuff that leads to a complete compromise," said cyber-risk analyst Chris Vickery.
Both ES&S and its main competitor, Dominion Voting Systems, have released voting machines that security experts say can add votes to paper ballots after they are cast by voters.
Together, these two companies sell and maintain 80 percent of U.S. voting systems.
Despite long-standing reassurances by vendors and election officials that voting machines cannot be hacked because they are not connected to the internet, recent security reports reveal that many voting machines are connected to the internet and possibly have been for years. Security experts are alarmed at internet connectivity in voting systems because it can allow hackers to inject malware that disrupts or changes the outcome of an election.
Kevin Skoglund, the lead researcher of one study, confirmed that vendors "know their systems are connecting through the internet."
In August, North Carolina became the latest casualty. Voters and representatives from good-government groups pleaded with the state board of elections to adopt the type of voting system almost unanimously supported by election security experts, one that uses hand-marked paper ballots. They asked the board to reject ballot-marking devices that use barcodes and argued that hand-marked paper ballots are more secure, less expensive and less likely to create long lines at the polls.
Nevertheless, Democratic chair Damon Circosta reached across the aisle to join two Republican commissioners in opening the North Carolina market to a barcode ballot-marking system. The vote presents a setback to a multi-year effort to provide secure, accurate elections for North Carolina voters.
Similar decisions have been made in Delaware, Georgia, Kansas, New York, Pennsylvania and Wisconsin. Communities in those states have experienced frustration, outrage and even launched investigations following certification or adoption of election systems opposed by experts, good-government groups, competing vendors and the general public. South Carolina lawmakers initially balked at the high price and poor security of new voting machines but eventually capitulated.
Some of these systems have subsequently had disastrous debuts, as in the case of Johnson County, Kansas, where, after spending $10.5 million on a new touch screen barcode voting system, the county experienced an election night alternately called a debacle and a fiasco.
How are vendors achieving these wins against such strong opposition? Jennifer Cohn, an election security advocate, has detailed many of the techniques being used. They include deep ties to powerful political players, targeted donations to political parties and their leaders, and cozy relationships with election officials that can include gifts, dining and travel. The newly released Philadelphia City Controller's report details conflicts of interest that resulted in a $2.9 million fine for the vendor, but the $29 million voting machine contract remains intact.
Are these insecure voting systems actually leading to incorrect election results? Perhaps. A 2015 election in Memphis, Tenn., underreported votes in four predominantly black precincts; data suggest over 100,000 votes may be missing from a Georgia election held last year.
The Senate has passed $250 million in funding for election security. Missing from the bill? Any language requiring strong security. Legislation has been proposed that would put real safeguards in place for our elections. It is even more imperative that it be passed now.